What Is Access Certification?
Access certification, also called an access review or user access review, is a periodic check of who has access to what. A reviewer looks at each user's access and makes one of two decisions: approve, if the person still needs it, or revoke, if they do not.
A group of these reviews run together, for example "all access to the core banking application, reviewed by its owner this quarter", is called a certification campaign. Common reviewer models are:
- Manager review: each manager reviews the access held by the people who report to them.
- Application or role owner review: the owner of an application or role reviews everyone who holds it.
- Designated reviewer: a named person, such as a compliance or security lead, reviews a specific scope.
Regulators expect this control. RBI, SEBI's Cybersecurity and Cyber Resilience Framework (CSCRF) and IRDAI all expect regulated entities to review user access periodically, and the DPDP Rules name access control and review among the minimum safeguards for personal data. We cover these requirements in more detail in our articles on RBI, SEBI and IRDAI audits and the DPDP Act implementation checklist.
Why Access Reviews Get Rubber-Stamped
Rubber-stamping is rarely carelessness. It is usually the result of how the review was set up. These are the five most common causes.
1. Too Much to Review at Once
A manager with a team of 25 people can easily receive a list of 2,000 or more access items, covering every application, group and permission each person holds. Nobody can make 2,000 careful decisions in an afternoon. When the list is that long, approving everything becomes the only practical way to finish on time.
2. No Context for the Reviewer
Access is often stored under technical names such as GRP_FIN_RW_07 or SAP_Z_FI_POST. A business manager cannot tell from that name what the access allows, whether it is sensitive, or whether the person has used it recently. Faced with something they do not understand, most reviewers choose the option that will not disrupt anyone's work: approve.
3. "Approve All" Is the Easy Way Out
Bulk actions are necessary at enterprise scale. Without them, large campaigns would never finish. But if an "Approve All" button is the most visible option and there is no follow-up on how it is used, it can turn the review into a single click. A campaign where 100% of items were approved in a few seconds is a warning sign in itself.
4. Revoked Access Is Not Actually Removed
In spreadsheet-based reviews, a "revoke" decision is a note in a cell. Someone then has to raise a ticket, and someone else has to remove the access in Active Directory or the application. If that chain breaks, the access stays. Reviewers notice when their revoke decisions have no effect, and they stop making them.
5. Accounts Without an Owner Are Never Reviewed
Certification campaigns are built from identities: each person's access is sent to their reviewer. Accounts that are not linked to any person, such as old service accounts, test accounts or accounts left behind by former employees, have no reviewer. They never appear in a campaign, which means some of the riskiest accounts are never reviewed at all.
How to Design Access Reviews That Actually Work
The fixes below do not require reviewers to work harder. They make the right decision easier than the lazy one.
1. Narrow the Scope of Each Campaign
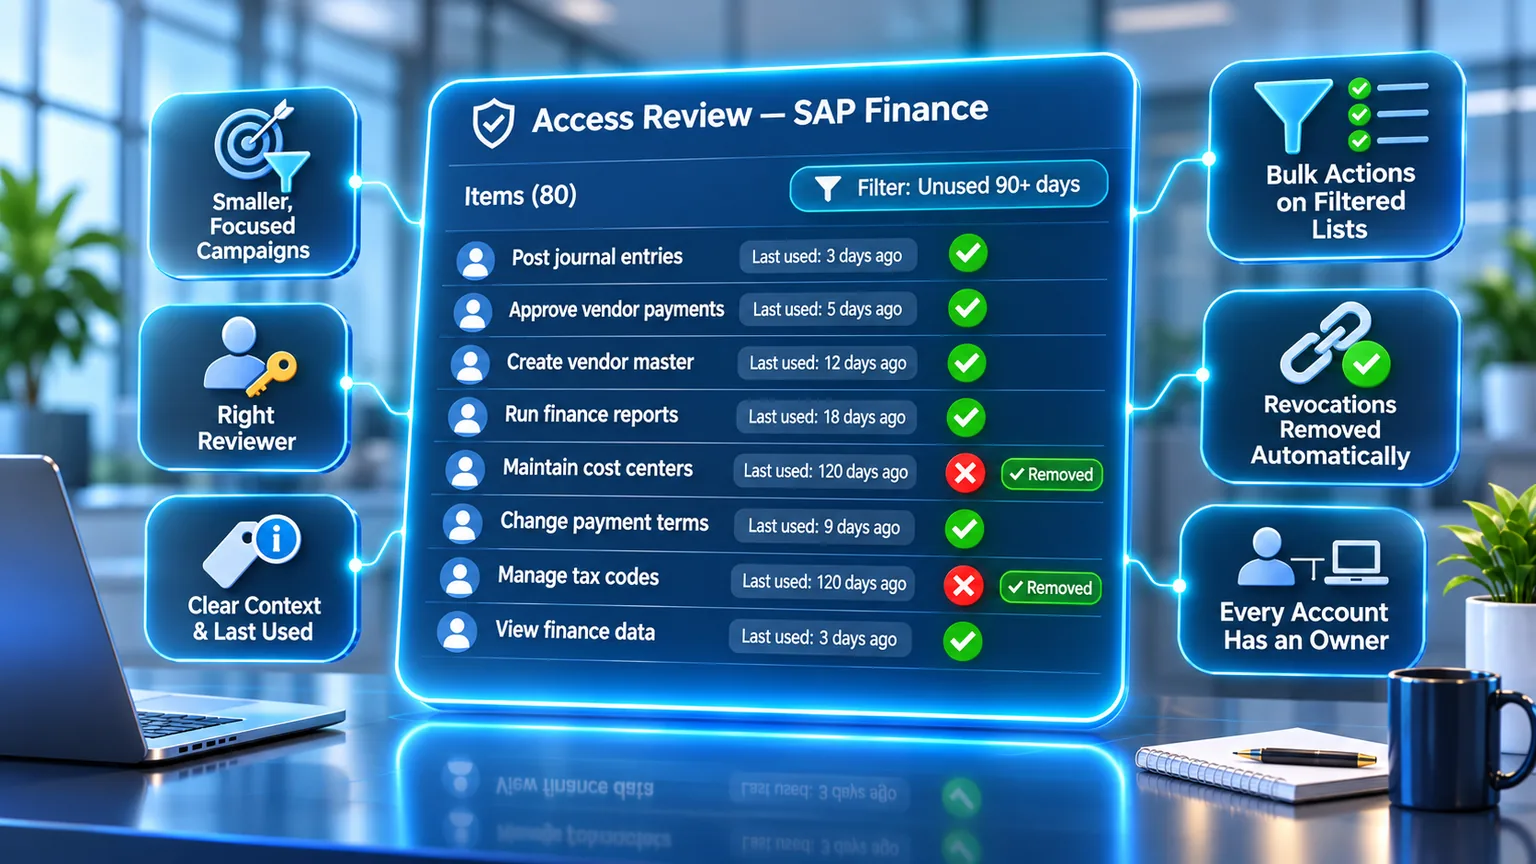
Instead of one review of "all access for all users", run smaller campaigns: one per critical application, one for privileged access, one for roles. A reviewer who receives 80 relevant items will make far better decisions than one who receives 2,000 mixed ones. Review high-risk systems more often, for example quarterly, and lower-risk systems less often.
2. Send Each Item to the Right Reviewer
Managers know what a person's job needs. Application owners know what a permission inside their application allows. Use manager reviews for broad access, and owner reviews for sensitive applications and entitlements. When the reviewer understands the item, they are more likely to question it.
3. Give Reviewers the Context to Decide
Replace technical names with business-friendly descriptions, so that SAP_Z_FI_POST becomes "Post journal entries in SAP Finance". Where possible, show when the access was granted and when it was last used. Access that has not been used in 90 days is a natural candidate for removal.
4. Use Bulk Actions With Care
Keep bulk approve and bulk revoke, because they are essential for large campaigns. Encourage reviewers to use them on a filtered list, for example "approve all standard access for this team" or "revoke all access for people who have left", rather than on everything at once. Report on how bulk actions are used, so that a campaign where everything was approved in one click gets a second look.
The same caution applies to what happens when a campaign reaches its end date. Automatically approving every item that is still pending is a bulk approval that nobody made. For sensitive applications, leave pending items for reviewers to decide, and make sure they are told that action is still required.
5. Close the Loop on Revocations
A revoke decision should trigger removal of the access automatically, through a connector to the application or a ticket for applications that cannot be connected directly. The result of each revocation, whether it succeeded, failed or is waiting on a ticket, should be visible, and failures should be retried and followed up. This is what turns a review into a control that auditors can rely on.
6. Clean Up Unlinked Accounts Before the Campaign
Before a campaign starts, find accounts in each application that are not linked to any person. Link each one to its rightful owner, assign an owner to genuine service accounts, and disable the rest. Once accounts are linked, they appear in reviews like any other access.
Rubber-Stamped vs Effective Review
| Area | Rubber-stamped review | Effective review |
|---|---|---|
| Scope | All access, all users, once a year | Focused campaigns by application, role or risk |
| Reviewer | Whoever is easiest to assign | The manager or owner who understands the access |
| Information | Technical names only | Business descriptions and usage context |
| Bulk actions | One click approves everything | Used on filtered lists, and reported on |
| Revocation | A note in a spreadsheet | Access removed in the target system, with status tracked |
| Evidence | Emails and spreadsheets assembled before the audit | Decision reports and audit trail exported straight from the campaign |
What to Look for in an Access Certification Tool
If your reviews still run on spreadsheets and email, an Identity Governance and Administration (IGA) platform can automate most of the work. When evaluating one, check whether it can:
- Run scheduled campaigns, for example quarterly or half-yearly, without manual setup each cycle
- Scope campaigns by applications, roles, entitlements and user groups
- Route items to managers, application owners or role owners
- Collect the data automatically from connected applications, including very large ones
- Offer bulk approve and revoke on filtered lists
- Remove revoked access automatically, with a ticketing fallback for applications without APIs
- Track the status of every revocation and retry failures
- Export reviewer records and the full audit trail of each campaign as audit-ready reports
Final Considerations
Access certification works when it is treated as a routine control rather than a once-a-year exercise before the audit. Smaller campaigns, the right reviewers, clear information and revocations that actually take effect will do more for your security posture than a larger review that everyone approves.
IamLogic IGA runs scheduled certification campaigns across applications, roles, entitlements and permissions, with reviews assigned to managers, application owners or role owners. Reviewers can approve or revoke selected items or a whole filtered list, with usage context shown alongside each item so that unused access stands out. Orphan and dormant account reports help you find accounts that are not linked to anyone before a campaign starts. Every reviewer is emailed when a review run is ready. When a campaign passes its end date, you choose the default: pending items can be approved automatically, or left untouched while reviewers are emailed that action is required and must log in to make their decisions. Revocations are carried out through connectors or, for applications without APIs, through ticketing integration, with the result of each one tracked and failed revocations available to re-run. Reviewer records can be exported as a report, and after the review the audit trail can be exported too, giving your auditors a complete record. A capital markets exchange used this approach to replace an email-based quarterly review, as described in our access certification case study.