The IamLogic platform
Access and governance were never separate problems.
Vendors split identity into products; auditors and attackers never did. IamLogic's two products work as one platform: sign in to IamLogic IGA with Access Manager single sign-on, and manage Access Manager users and groups from IGA through a built-in connector.
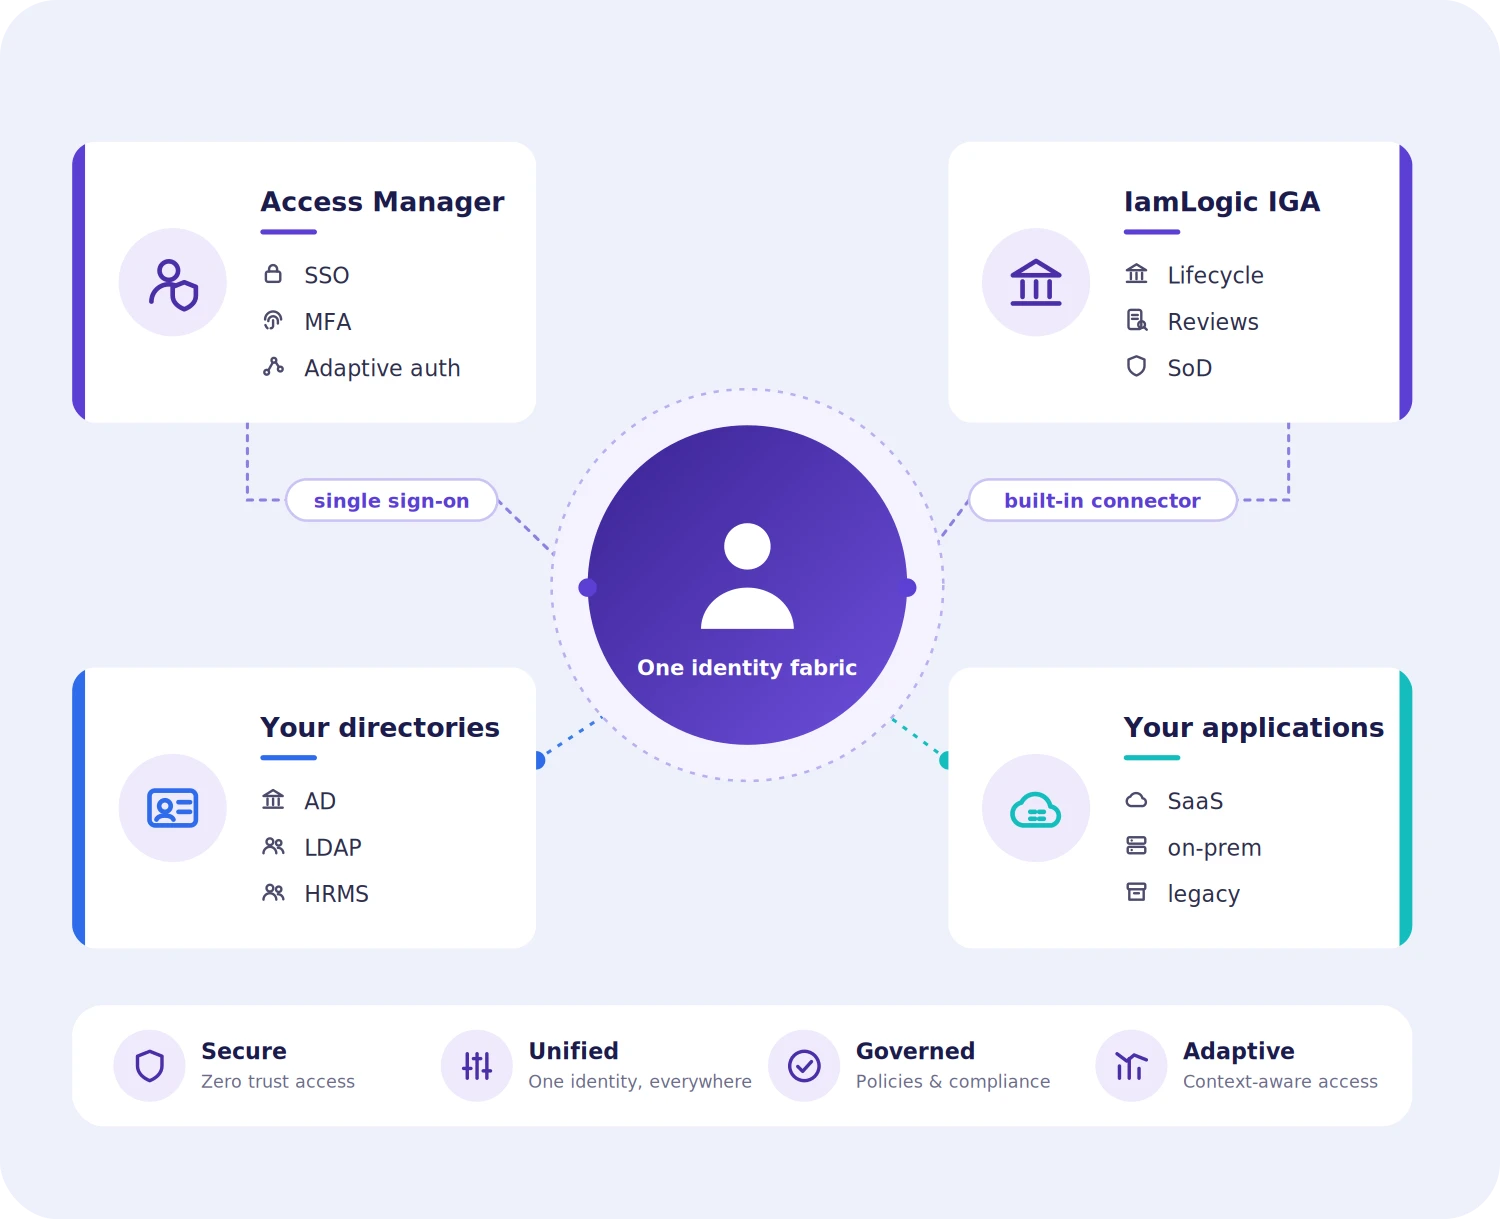
Better together
What the combination buys you
Each product stands alone. Together, they close the loop that point solutions leave open.
Single sign-on into governance
Reviewers and administrators sign in to IamLogic IGA with Access Manager single sign-on — SAML, OpenID Connect or RADIUS — the same way they sign in to every other application.
Governance decisions enforce at login
When IGA revokes access, changes a role or expires a contractor, the change is sent to Access Manager straight away and applies at the user's next sign-in — no manual sync needed. The front door and the rulebook stay consistent.
One audit trail across both
Who authenticated, with which factor, to which application, holding which approved entitlements, last reviewed when. One correlated narrative for auditors instead of four exports.
One vendor, one deployment, one support line
Same connector framework, same deployment models, same Bengaluru-based engineers on support. Connecting the two takes an OAuth client in Access Manager and a few connector fields in IGA.
Architecture principles
Engineered for regulated, heterogeneous, Indian enterprise estates
- Deployment freedom: on-premises, private cloud or public cloud — identical product, HA and DR topologies supported.
- Data sovereignty: identity data, credentials and logs can remain entirely within your infrastructure in India.
- Python extensibility: authentication policies and application connectors are scriptable — your edge cases don't wait for our roadmap.
- Legacy reality: browser-extension SSO and ticketing-workflow provisioning cover the applications that federation and APIs never will.
- Evidence by default: every decision — human or automated — is logged for traceability.
Where to start
Start with your most urgent gap
Audit finding on access reviews or orphan accounts?
Start with IamLogic IGA — certifications and lifecycle automation first.
VPN without MFA, or legacy apps outside SSO?
Start with Access Manager — the front door closes fastest.
Greenfield identity programme (DPDP-driven)?
Deploy both — the DPDP mapping spans access control and governance.
See IamLogic on your own applications
A 30-minute walkthrough of Access Manager and IamLogic IGA, mapped to your environment, your applications and your compliance obligations.